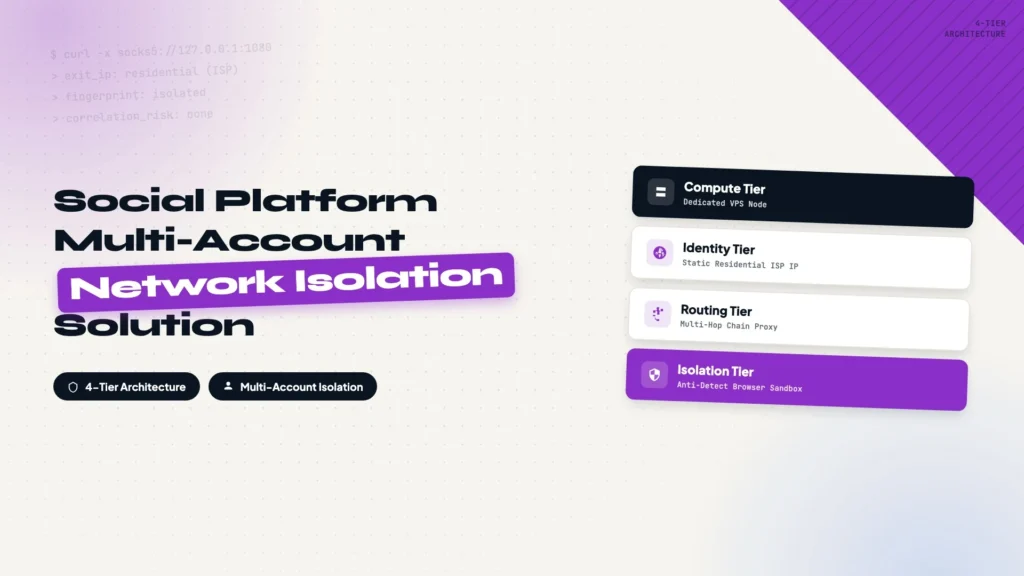
Core Challenges and Objectives of Multi-Account Operations
In cross-border e-commerce, brand matrix management, and social media agency operations, managing multiple accounts across international platforms is standard practice. However, operating multiple profiles on a shared network or device inevitably triggers modern anti-fraud algorithms. When platforms detect overlapping network fingerprints and hardware signatures among supposedly independent accounts, they correlate them as unified risk entities—often leading to batch throttling, shadowbanning, or account suspension.
Modern anti-fraud systems on platforms like TikTok, Meta (Facebook/Instagram), and X continuously analyze multidimensional telemetry in the background. If separate business accounts share consistent networking routes or device parameters, automated safety systems classify them as coordinated activity regardless of content legitimacy.
This engineering guide outlines a robust, modular framework designed to provide each account with a dedicated, persistent, and entirely isolated digital fingerprint and network route.
The Four-Tier Network Isolation Architecture
This isolation framework comprises four specialized technical tiers. Each tier addresses a distinct attack vector in platform risk detection, working in synergy to provide comprehensive operational security:
Social Platform Risk Detection and Correlation Mechanics
Understanding platform risk modeling clarifies why isolated networking is essential. Modern anti-abuse engines rely primarily on four telemetry vectors:
| Risk Vector | Detection Mechanism & Correlation Logic |
|---|---|
| IP Address & Allocation Type | Logging into multiple accounts from the same IP—particularly shared datacenter subnets—is the most immediate flag for automated operations. |
| Device & Browser Fingerprinting | Canvas/WebGL hashes, system font enumeration, screen resolution, audio stack, and timezone metadata aggregate into a deterministic hardware identifier. |
| Behavioral Telemetry | Keystroke cadence, cursor velocity, click intervals, and active session windows are monitored for non-human or automated behavior. |
| Shared Metadata & Business Credentials | Identical phone numbers, billing cards, recovery emails, or ad accounts establish direct administrative linkage. |
Why Architecture Must Follow a Strict Build Order
The four tiers possess strict architectural dependencies and must be deployed sequentially:
Compliance Guidelines and Legitimate Use
This architecture is designed for legitimate business infrastructure—enabling cross-border marketing teams, regional brand divisions, and agencies to operate distributed commercial assets without interference from shared IP pollution. All configurations should strictly comply with local regulatory standards and platform terms of service.
Begin with the first guide below to deploy your dedicated high-speed transit node.